
Amazon Web Services (AWS) has announced a significant expansion of its Amazon Elastic Block Store (Amazon EBS) Volume Clones feature, introducing cross-account copy capabilities designed to streamline development, testing, and data management workflows across enterprise environments. Building upon the instant point-in-time copy functionality introduced last year within single Availability Zones, this latest update allows organizations to securely replicate and re-encrypt EBS volumes across separate AWS accounts.
The new capability addresses a common operational challenge for engineering and infrastructure teams: how to safely utilize up-to-date production application data in secondary environments—such as staging, testing, and sandbox accounts—without compromising the strict isolation and security of production workloads. By enabling cross-account copies, AWS is empowering businesses to maintain distinct boundaries between production and non-production environments while still benefiting from real-world data fidelity during the development lifecycle.
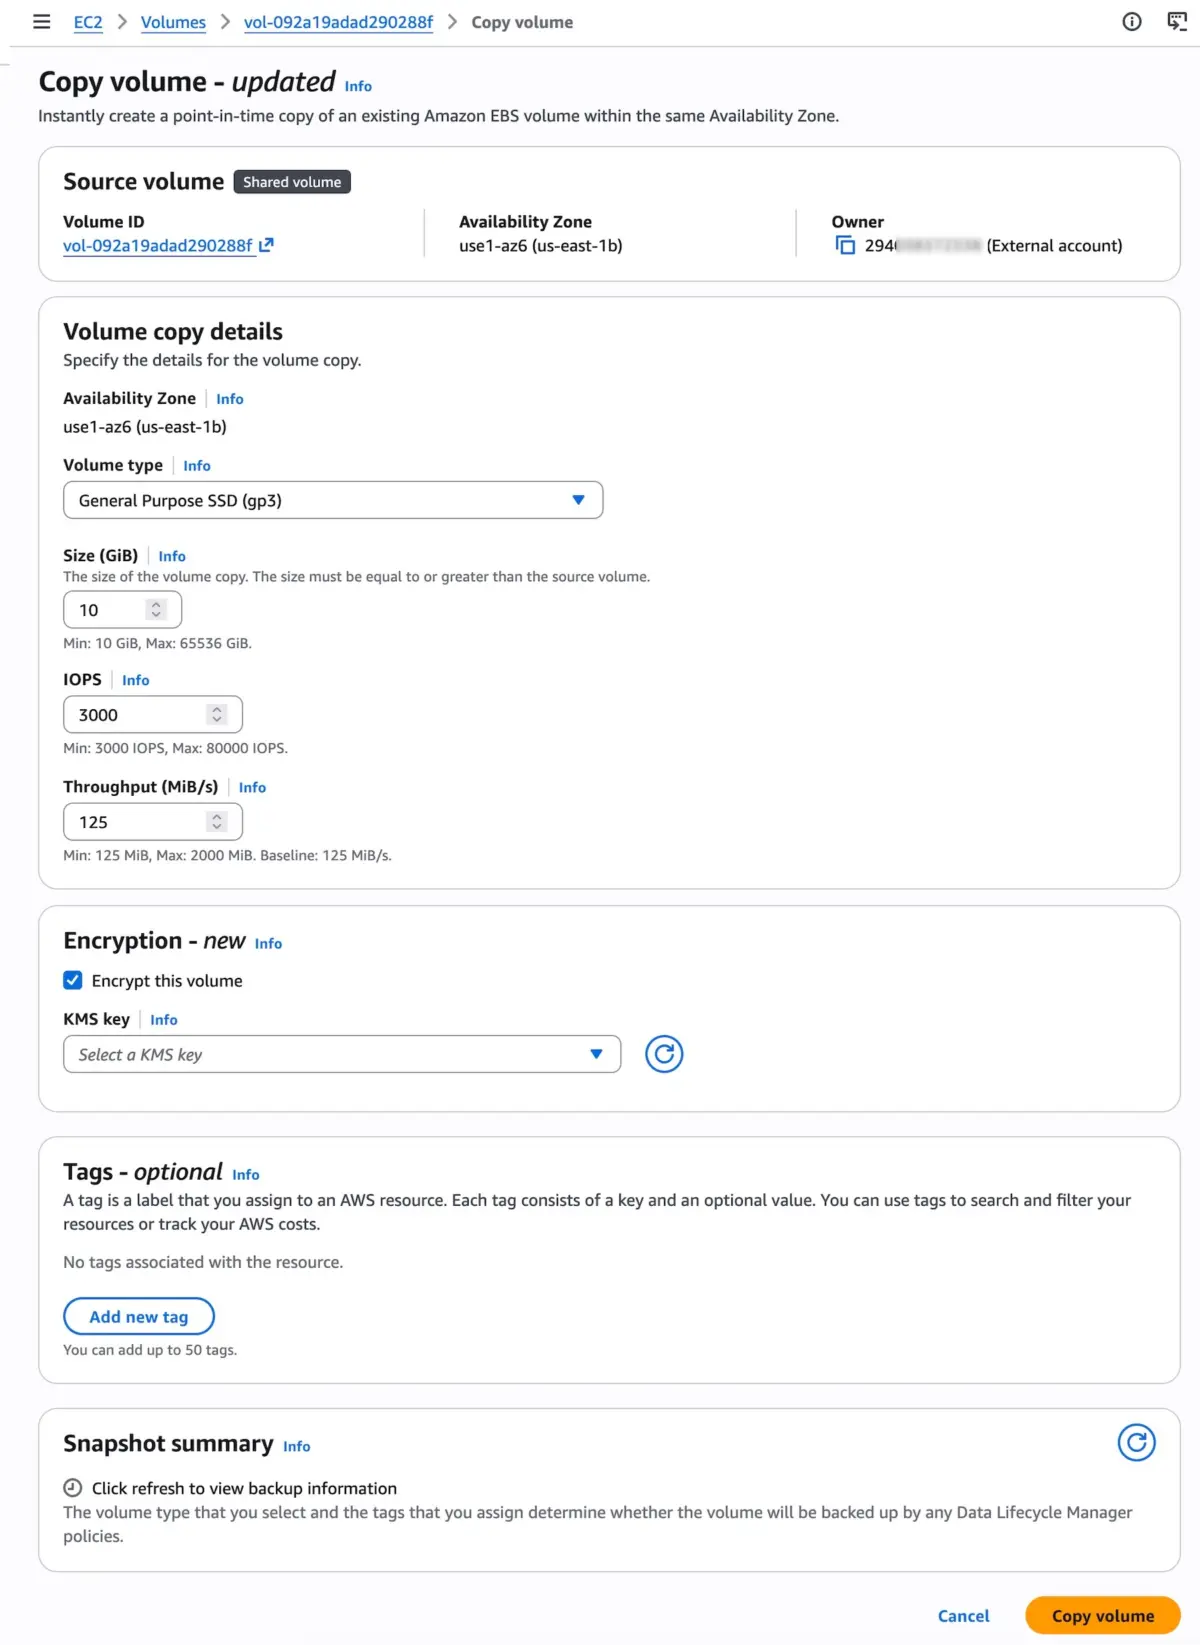
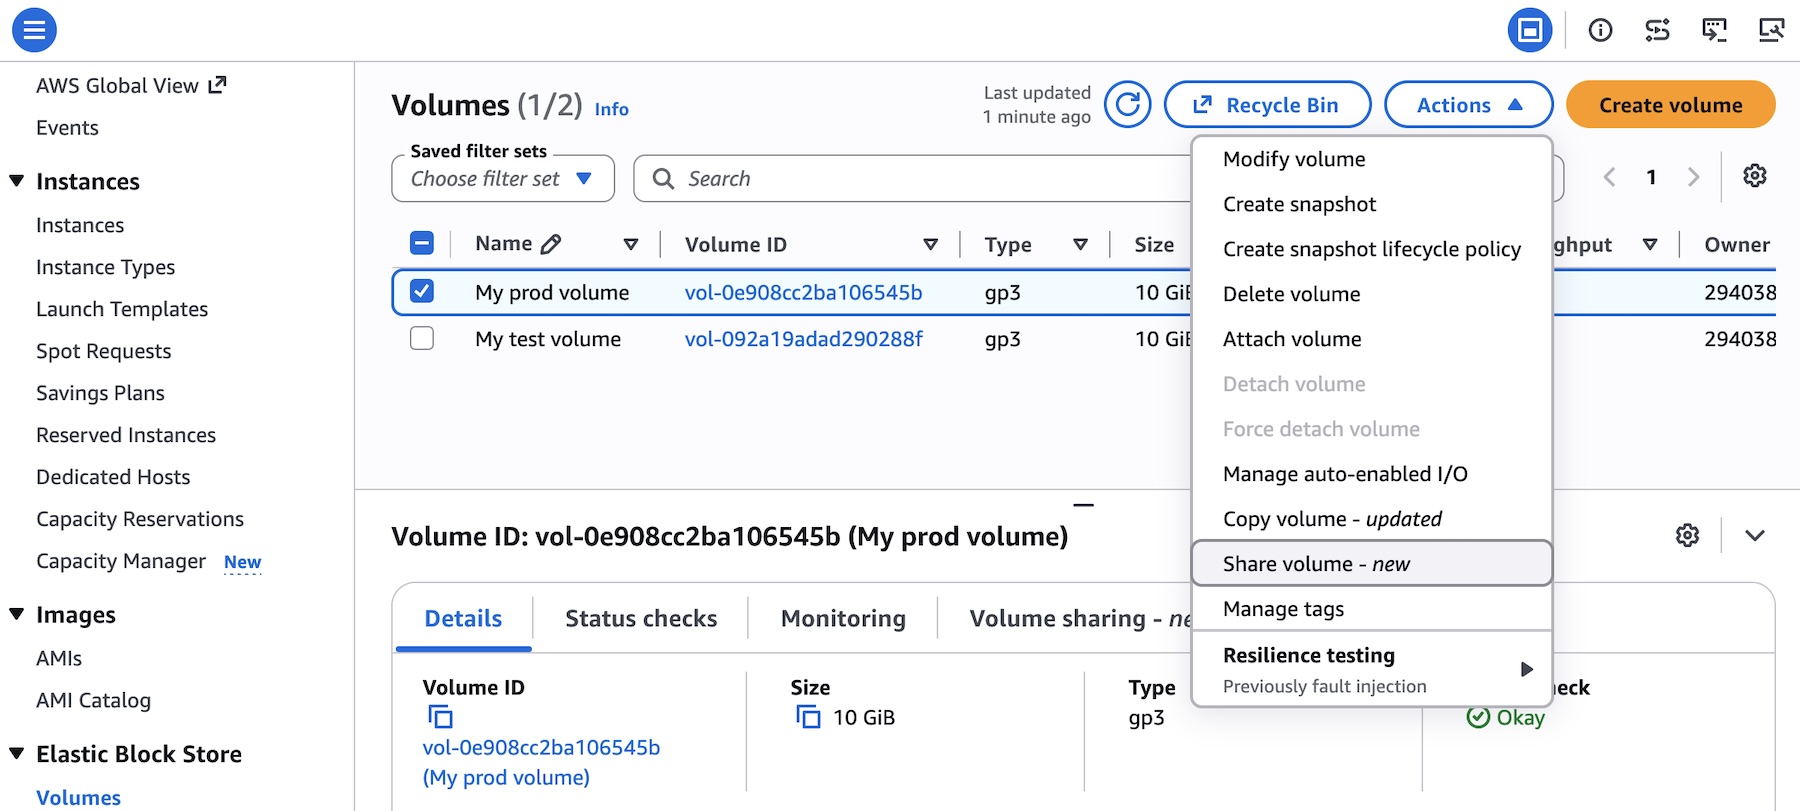
The process of moving and duplicating data across accounts leverages AWS Resource Access Manager (RAM), a service built to facilitate secure resource sharing across AWS accounts and within broader AWS Organizations. To initiate a cross-account copy, the owner of the source EBS volume grants the designated target account access through the AWS RAM console or by integrating the volume into existing resource shares. Once the target account accepts the shared resource, administrators can view the volume directly within their local Amazon EBS console interface and execute a copy command.

A key security and operational benefit of this new feature is the ability to optionally re-encrypt the volume during the copy process. Target accounts can apply their own AWS Key Management Service (AWS KMS) keys to the newly generated volume copy. This ensures that organizations maintain strict cryptographic governance, adhering to internal compliance mandates and security best practices even when data moves across administrative boundaries within a multi-account cloud architecture.
For engineering teams looking to automate these workflows, the cross-account sharing and copying functions can also be managed programmatically. Developers can leverage APIs alongside tools such as the AWS MCP Server and associated plugins within their preferred AI coding environments to discover documentation, construct API calls, and streamline infrastructure management tasks.
The introduction of cross-account volume clones arrives as organizations increasingly adopt multi-account strategies via AWS Organizations to isolate workloads, manage billing, and enforce granular security permissions. In such architectures, keeping development and test environments synchronized with production data has traditionally required complex snapshot-sharing workflows, manual volume restoration, or custom scripting. By streamlining this capability directly into the EBS Volume Clones framework, AWS is reducing administrative overhead and accelerating the feedback loops required for rapid software delivery.
Cross-account volume clones for Amazon EBS are available immediately in all AWS Regions that currently support Amazon EBS Volume Clones. Organizations seeking detailed regional availability information or looking to review future service roadmaps can consult the AWS Capabilities by Region documentation. Engineering teams can begin utilizing the feature immediately through the Amazon EC2 console, with feedback channels open via AWS re:Post for Amazon EBS and standard AWS Support pathways.